kaleidoscopic
Internet wanderer with a wobbly front tooth. Cat named Pickle.
If my tooth falls out: I’ll put it under my pillow, in the morning it will emerge as a butterfly – or a household appliance of your choosing. Make a wish for it.
Profile background: Maple Color (Erin Hanson, 2019).
I routinely block anti-AI accounts, partly because too many anti-AI protestors are worse than chatbots from a decade ago.
- 0 Posts
- 7 Comments
@thenextguy odd, my post two days ago is not visible in Lemmy.
What am I missing?
@thenextguy please, what made you assume OpenAI?
I think it likely that the developer chose the name.
If he did gain assistance from AI, for the name, the likelihood would be Anthropic (not OpenAI).
https://tinyurl.com/da-avapet – note the use of Claude.
@hucste nice, I always like his writing.
The narrowness of the text column can make things unnecessarily difficult to read.
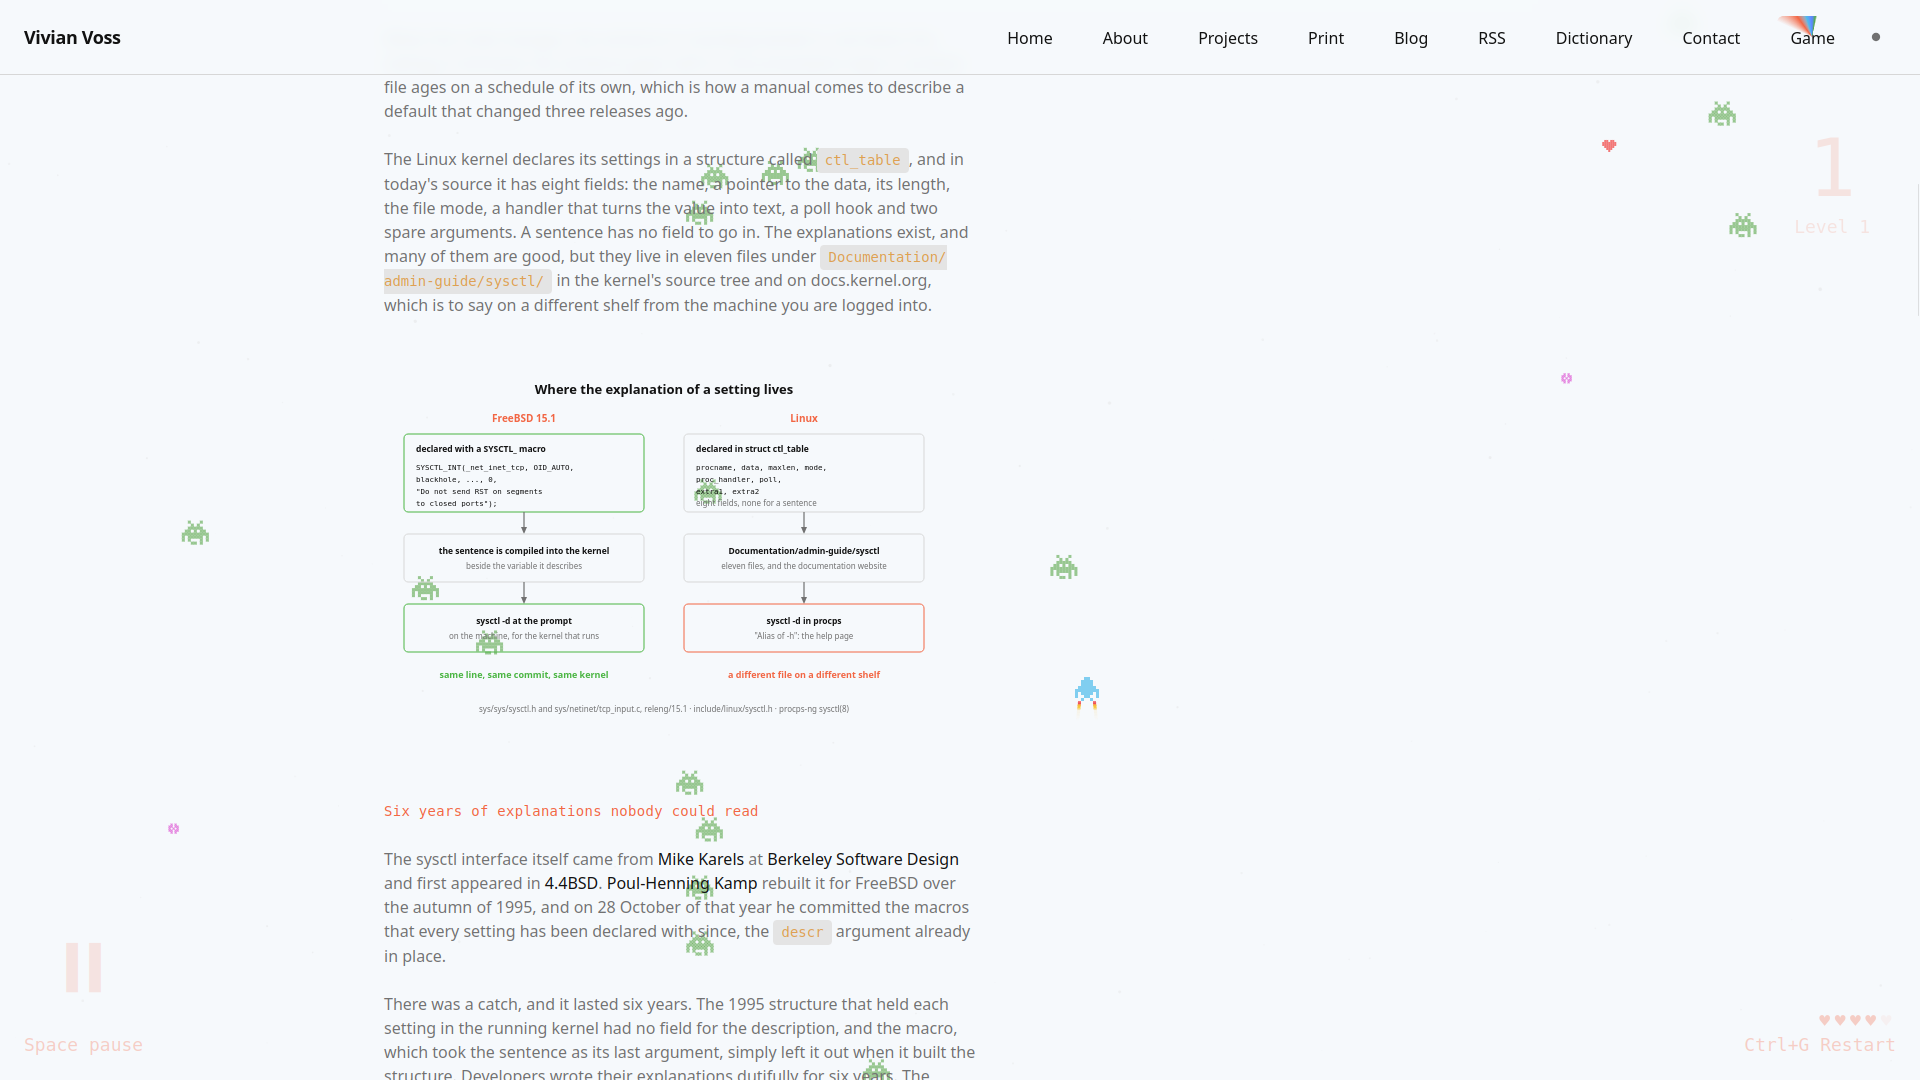
The screenshot here is referenced from discussion in LinkedIn, https://www.linkedin.com/feed/update/urn:li:activity:7514237399435169793/
@hucste I usually like his writing.
This one describes freebsd-update without mentioning pkgbase.
@hucste thanks for sharing this. It’s a good read, and I like that it says plainly that QEMU with KVM uses the same one-process-per-guest design.
The author acknowledges use of AI, so I used AI for what’s below.
A few things that a Linux-leaning reader might push back on:
The headline numbers don’t compare like with like. The table sets 46,709 lines of bhyve against 1,969,575 lines of QEMU across all targets, but QEMU is a multi-architecture emulator as well as a KVM front end. The post does give the x86 target (57,039 lines) and hw/ (644,480 lines), but only in the closing summary, not in the table people will screenshot.
The minimal-hypervisor idea is already common on Linux, and the post doesn’t mention it. Firecracker, Cloud Hypervisor and crosvm all run on KVM and deliberately offer very few devices. Many Linux readers will probably think “so, Firecracker”.
The post’s own example works against its line-count argument. The October workaround shows that what matters is which devices a guest is given, not how much device code is compiled in. QEMU works the same way: a floppy controller the guest never sees can’t be attacked. VENOM is a fair point from 2015, but you can configure that risk away rather than needing a smaller codebase.
Confinement on Linux is often on by default too. The post says bhyve usually runs as root and confines itself with Capsicum by default. On Linux, libvirt typically runs QEMU as an unprivileged user and confines it with SELinux or AppArmor (sVirt) on the major distributions. Capsicum’s self-imposed design is admirable, but “on by default” isn’t unique to FreeBSD.
Linux users tend to weigh the whole stack around the hypervisor: libvirt, Proxmox, OpenStack, live migration, GPU passthrough, nested virtualisation. The post measures tidiness, not the tools available around it. I haven’t checked where bhyve stands on all of those today, but readers will ask.